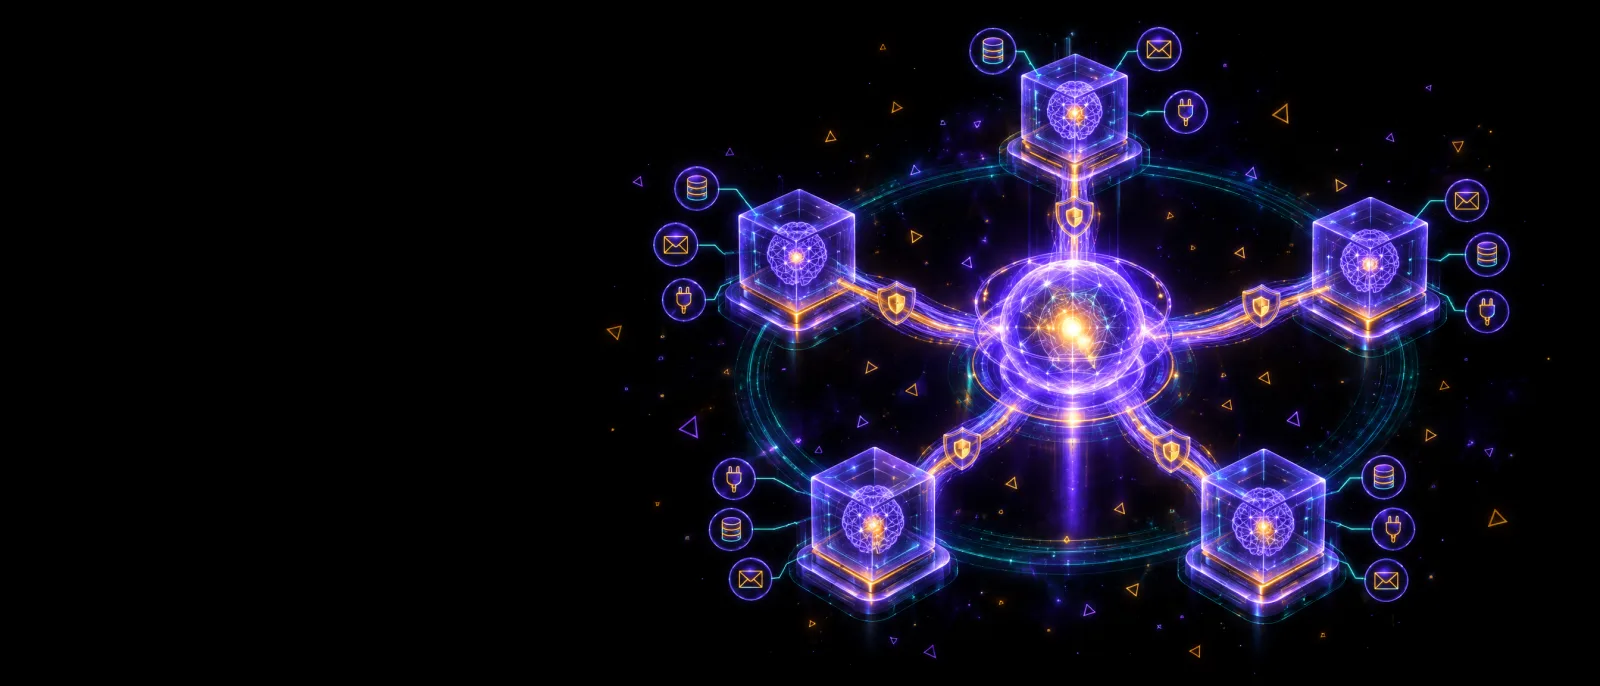
One agent is a demo. A system of agents is a workforce.
Orchestration, shared memory, tool access and permissions, engineered once and reused by every agent you ship after the first.
One call with a senior engineer. A straight answer on what it would take.
Where you are. Where you’ll be.
You need this if
- You have three agent projects and three different stacks
- Security can't tell you what your agents can access
- Model costs are growing faster than the value they produce
What changes for your business
- Each new agent ships in weeks because the hard parts already exist
- Every action is traceable to an agent, a tool call and a permission
- Swap models or vendors without rewriting your agents
What we hand over
- Orchestration layer for planner, worker and reviewer agents
- Tool registry with per-agent scopes and approval gates
- Shared memory, retrieval and context management
- Tracing, evals and cost dashboards per agent and per task
What it is
Multi-agent orchestration is the shared layer that lets several AI agents work as one system: it routes tasks between them, controls which tools and data each may use, shares memory, and records every step. Without it, every new agent is a separate project with its own keys, logging and security gaps.
The second agent is where most programs fall apart. Each team wires its own prompts, its own API keys and its own logging, and six months later nobody can say what any agent is allowed to touch. We build the platform layer underneath: an orchestrator that routes work between specialist agents, a tool registry with scoped permissions, shared memory and retrieval, evaluation harnesses and full tracing. New agents become configuration, not projects.
- Why now
- 95% of generative AI pilots deliver no measurable P&L impact. MIT NANDA, The GenAI Divide, 2025 (opens in a new tab)
- Last reviewed
How it runs
- 01
Diagnose
Typically 2–4 weeksWe map the problem, your data and your systems, and agree the one number that defines success.
- 02
Prove
Typically 4–8 weeksA working pilot on your real data, measured against that number. Not a slide demo.
- 03
Ship
Scoped to the outcomeProduction build with security, monitoring, cost controls and documentation included, not upsold.
- 04
Run
Ongoing, optionalWe operate what we built against clear service levels, or train your team to. Your call. No lock-in.
Questions you’ll ask
- When do we need an orchestration platform rather than single agents?
- Usually at the second or third agent. Once separate teams are wiring their own prompts, keys and logging, security loses track of what agents can touch and costs stop being attributable. That's the moment a shared platform pays for itself.
- Do you build on a specific framework or vendor?
- We pick per estate, and we favour open, swappable components over a single vendor's closed stack. Models, vector stores and frameworks change every few months, so the platform is designed so any one of them can be replaced without rewriting your agents.
- How do you control what each agent is allowed to do?
- Every tool an agent can call is registered with scoped permissions, the agent runs under its own identity, and every call is traced. Risky actions route to a human approval step. Security can answer 'what can this agent access?' from one place.
Sound familiar? Let’s fix it.
One call with a senior engineer. You’ll leave with a straight answer on what it would take.
Let's Build Together